What ‘Read and Change All Your Data’ Really Means for a Browser Extension
A browser extension that asks to “read and change all your data on the websites you visit” sounds as though it wants the keys to your entire digital life. Sometimes the warning is appropriate for a useful tool: an ad blocker must inspect page content to block elements, a password manager must recognize login forms, and a translation tool must read text before it can translate it. The same permission can also give a careless or malicious extension far more reach than its simple feature appears to need.
The right response is neither automatic trust nor automatic panic. The warning describes a capability. Your job is to decide whether that capability matches the extension’s purpose, whether you trust the party receiving it, and whether you can reduce the access without breaking the feature you need.
What “site data” means in this warning
Web browsers separate extension abilities into permissions. Some concern browser features such as tabs, downloads, history, bookmarks, or the clipboard. Others, often called host or site permissions, determine which web pages an extension can interact with.
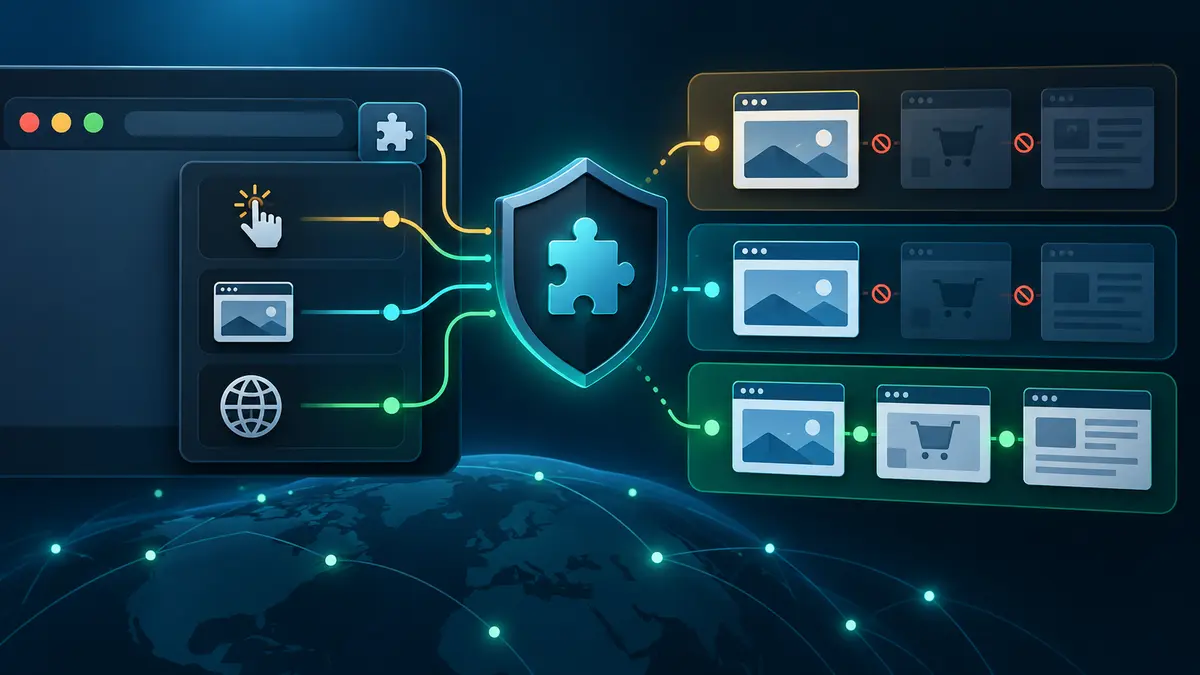
When an extension can read and change data on a site, it may be able to inspect or modify the content of matching pages while those pages are open. Depending on its code and other permissions, that can include text displayed on the page, form fields, links, page structure, and information the site makes available to the page. “All sites” means the permission is broad across the websites covered by the extension’s declared host access, not merely the extension developer’s own website.
That reach is why Google labels access to data on all visited websites as a meaningful permission. Its help documentation says such access can allow an extension to read, request, or modify data on pages, including sensitive sites. Mozilla similarly explains that extension APIs may allow an add-on to read or write data entered on web pages, use computer features, or alter browser settings.
The warning does not prove that an extension records everything it can reach. Capability and behavior are different. But you normally cannot watch every action the code takes, so permissions should be treated as the boundary of what you are allowing—not as a promise that the extension will use only a small part of that access.
What the warning does not automatically mean
It does not mean the extension can open every file on your computer, control every other app, or retrieve every password stored by the operating system. Those actions would require other permissions, browser vulnerabilities, native software, or additional access. It also does not mean the extension can read sites you never open simply because it has broad host permission.
However, “it is only inside the browser” is not a safe reason to dismiss the warning. People enter highly sensitive information into browsers: email, medical portals, business dashboards, payment pages, and private messages. An extension able to run on those pages occupies a trusted position even if it has no direct access to the rest of the computer.
Private or incognito mode is a separate setting in major browsers. Extensions are not necessarily allowed there by default, and enabling one for private windows expands where it can operate. Private browsing mainly changes what the browser stores locally; it is not a special security container that makes a permitted extension unable to see the page.
Why a legitimate extension may ask for broad access
Judge the request against the job. A tool that must change nearly every page may have a defensible reason for broad access:
- An ad or tracker blocker needs to observe page requests and remove or hide unwanted elements across many sites.
- A password manager needs to recognize sign-in forms and offer credentials where you choose to use it.
- An accessibility extension may restyle text, adjust contrast, or change page navigation.
- A writing assistant may examine text fields to offer spelling or grammar suggestions.
- A translation or read-aloud tool needs page content before it can process that content.
Now reverse the test. A calculator, new-tab wallpaper, simple clock, or single-site shortcut usually has a weaker reason to access every page you visit. That mismatch is not conclusive evidence of malware, but it is a reason to stop and investigate before installing.
Also consider whether the extension can work with narrower access. A tool designed for one service may need permission only on that service’s domain. A page-color tool may work perfectly when you activate it on the current tab. Convenience is a valid product choice, but it should not silently become unlimited access.
The three Chrome site-access choices are meaningfully different
Chrome can offer controls such as “when you select the extension,” “on this site,” or “on all sites.” The wording can vary slightly by version and device, but the practical distinction is useful.
When you select the extension
The extension receives access to the current site after you intentionally activate it. Google says that closing the tab or window means you must select the extension again. This is a good starting point for a tool you use occasionally, such as a color picker, page cleaner, or one-time formatter.
On a specific site
The extension can run automatically on the named site but not everywhere else. This suits tools tied to a work platform, webmail service, learning portal, or other limited set of domains. Add only the sites needed for the feature instead of treating “all sites” as the default.
On all sites
The extension can operate automatically across all matching websites. Some core features genuinely require this. Grant it only when the function makes sense everywhere and the developer has earned that level of trust.
Google notes an important limit: changing this site-data setting affects sites that match the extension’s host permissions. It does not control lower-level network access changed through VPN or proxy settings. If an extension also configures a proxy, review that behavior separately.
A five-minute permission audit
Open the browser’s extension management page rather than relying only on icons pinned to the toolbar. In Chrome, open the Extensions menu and choose Manage extensions. In Firefox, open Add-ons and themes, then Extensions. Names move occasionally, but every mainstream desktop browser provides a page showing installed add-ons.
1. Remove what you do not use
An unused extension delivers no benefit but may retain its permissions. If you cannot remember why you installed it or have not used it in months, removal is usually clearer than leaving it disabled indefinitely. You can reinstall a legitimate tool later if you actually need it.
2. Compare the permission with the feature
Read the extension’s store description and its own explanation of permissions. Ask a literal question: what feature would fail if this permission were removed? If a coupon tool needs shopping-site access, that relationship is visible. If it asks for access to every site including email and banking, look for a credible explanation and a narrower setting.
3. Verify the developer, not just the name and icon
Look at the publisher identity, official website, privacy information, update history, user base, and recent reviews. Similar names and copied icons can mislead. Reach the store listing from the browser’s management page when possible instead of choosing the first search result.
Mozilla advises comparing requested permissions with the extension’s features and checking whether the developer explains the need. It also warns that automated scanning or human review does not guarantee absolute safety. Store presence is useful evidence, but it is not a permanent warranty.
4. Reduce site access and test the result
Change “all sites” to “when selected” or a short list of specific sites. Then use the extension normally. If its essential feature works, you have reduced exposure without giving up the benefit. If it fails, decide whether broader access is genuinely worth granting; do not expand it reflexively just to silence an error.
5. Check private-window access separately
Leave private or incognito access off unless you have a clear reason to enable it. If you use private browsing for sensitive or separated activity, allowing a broad extension there may undermine the separation you expected.
Updates can change the trust decision
An extension is software that continues to change. A new version may add a feature, request another permission, change ownership, or alter its data practices. Browsers may show a new warning or disable an extension until you approve expanded access. Do not click through simply because the tool was safe or familiar when you first installed it.
Read the new request as if you were installing the extension today. Does the update explain the need? Does the publisher still match? Are recent reviews describing unexpected redirects, ads, search changes, or new data collection? A legitimate acquisition or feature change can still make the new tradeoff wrong for you.
Periodic reviews matter because extensions can outlive the task that justified them. A conference add-on, temporary screen recorder, shopping helper, or old development tool should not remain a permanent observer of your browsing by accident.
If you suspect an extension has misused access
Start by disabling the extension. This quickly stops it from running while you preserve its name and details for your notes. Record the publisher, version, permissions, install source, and any suspicious behavior. Then remove it through the browser’s extension manager.
If the browser says the extension is controlled by an administrator or keeps returning after removal, check whether the device is managed by your employer or school. On a personal computer, persistent reinstallation or policy settings you did not configure may justify a reputable malware scan and professional help.
Next, match the cleanup to what happened. If you entered a password on a page while a suspicious broad-access extension was active, change that password from a clean browser or another trusted device. Start with email and other accounts that can reset additional services. Review active sessions, connected apps, recovery details, and important transactions. NerveFilter’s guide to what to do after clicking a suspicious link includes a similar evidence-based triage principle: respond to the access or information actually exposed rather than performing random cleanup steps.
If you merely installed the extension but never granted the requested access, never activated it, and saw no suspicious account activity, the response may be limited to removal and review. Do not announce that every account is compromised without evidence. At the same time, do not assume uninstalling reverses information already collected. If an extension required you to create an online account or connect another service, review that connection separately; uninstalling software may not revoke its online account access.
A simple decision test before you install
Put the extension through three gates:
- Need: Is the feature useful enough to install software for, or can the browser or website already do it?
- Fit: Do the requested permissions have a direct, understandable relationship to that feature?
- Trust: Is the publisher identifiable, is the extension maintained, and do its privacy explanation and recent behavior support granting that access?
If the extension fails one gate, pause. Search for a narrower alternative, use the website version of the tool, or grant access only when clicked. The best permission is not always “none”; it is the smallest access that supports a feature you genuinely value.
Browser warnings are deliberately broad because the browser cannot summarize every future action an extension might take. Translate the warning into a practical question: “Which pages can this tool enter, what could it do there, and why should this developer be allowed to do it?” Once you ask that, the scary sentence becomes a decision you can manage.
Official sources